Compliance or Security…don’t make the wrong choice
Your company was successfully audited against security standards and yet, a breach still happened. Why? Compliance does not mean your cyber security is working for you.
This is the uncomfortable question your business will have to deal with.

You have ISO 27001.
You have Cyber Essentials and Cyber Essentials Plus. Perhaps GDPR compliance or perhaps you align to PCI-DSS. Whatever it is, we know that the policies are written.
The controls are documented.
The badges are added to the website and certificates hang on the wall. But the cybercriminals don’t see badges and certificates the same way you do. They simply don’t care. However, you should!
So, what do the criminals see?
Indeed, you might need these certifications for a client contract or government work.
The misconfigured cloud storage.
The unmonitored service account.
The MFA exception that “temporarily” became permanent.
The user account over-provisioned with access rights logging in to admin account.
The unpatched operating system.
The firewall or VPN with a zero-day vulnerability.
This all means that your cyber security policy isn’t effectively implemented.
We speak with clients who see compliance as security and yet both achieve different goals. The two are not the same. Compliance proves you met a standard at a moment in time. A car MOT is a snapshot on that day to say it was ok. It is not a guarantee that you be safe for the next 12 months! Cyber Essentials is a point in time assessment but this does not mean you will be safe the following day or week.
The question is that one is a checklist – “Did we implement the control?”
The other is a capability – “Is the control effective?”
Are we exposed by something we should have?
But security proves you can withstand pressure in real time. An ongoing continuous effort to minimise risk and to protect users, data and systems.
A number of organisations who have been breached in the past were compliant with various standards:
Frameworks in place.
They followed the guidelines.
They passed the audits.
But they weren’t protected. However, they were compliant! Last year we saw an incredible number of high profile data breaches for some well known companies. Most had the right certifications and assurances. And yet, they were breached because they mistakenly assumed that certification meant good cyber security. It didn’t!
So what’s the real measure of your security maturity? The number of certifications… or the ability to protect, detect and respond before it is too late?
At what point does “good enough for the auditor” become dangerous for your business? The answer is very simple and it is the minute you believe that certification is enough. Does this sound like you?
Is compliance strengthening your security posture, or quietly giving you a false sense of security?
Or, would you like an honest review of your security posture? Not a tick box exercise over Teams, but in person where you look us in the eye and answer some tricky but relevant questions.
I found this image on Facebook.
Those of you who ride motorbikes will know that having that right gear all of the time, matters. If you ever come off a bike at speed, you will know what I mean. Your leathers will stop your skin being torn from your body. Underpants will not. Having suffered a high speed on the M6 (Honda Nighthawk 650 @ over the speed limit) I can assure you that the leather saved my legs…and life.
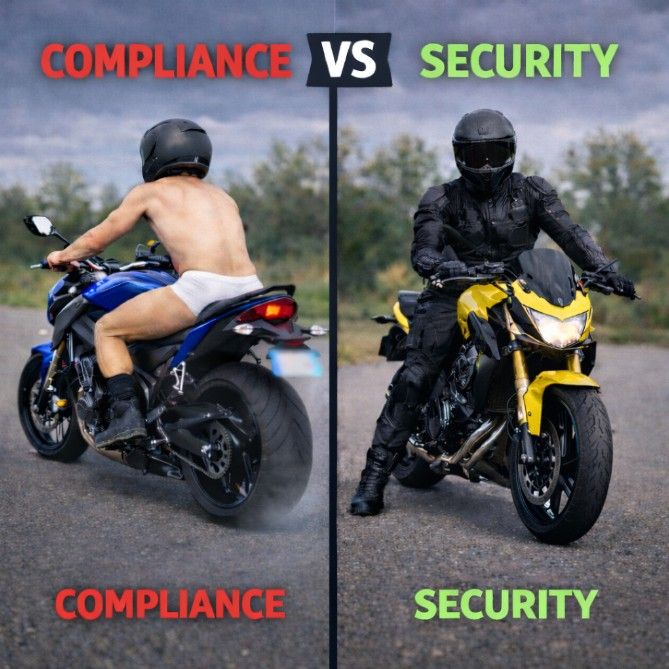
As a business, you will need certifications such as Cyber Essentials, ISO 27001 and DCC (Defence contractors) amongst others for commercial contracts. However, this will not keep you secure unless properly implemented. If you are attacked, the business will suffer skin loss in the form of data loss and damage to your reputation.
Security means compliance with implementation so all objectives are met.
Don’t be caught in your underpants.
We can be found on 03333 22 1011 where you will speak to a human being, no IVR, just us.
Leave a Reply